Blog
Threat/Vulnerability News
PHP2Shell: attacks before the patch, and automation by nightfall
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including what the attack tooling actually carried.

"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.
wp2shell in the Wild: From Patch to Mass Exploitation in Under 48 hours
The ELLIO Deception Network recorded more than 11,500 sessions across 700 sensors as traffic moved from probing to attempted database extraction, administrator creation, and a web-shell write. The first probe arrived the morning after WordPress published its fix.
Sanctioned, Seized, Still Scanning: Inside a Russian Bulletproof Hosting Network Targeting the EU
On 18 May 2026, Dutch investigators seized more than 800 servers and broke up a hosting operation that prosecutors say powered Russian cyberattacks across the EU. We had spent the previous year watching the same network from the other side. After the seizure, the scanning did not stop.
[watchdog]: Inside a Mirai variant with six-layer persistence
An open directory is serving a Mirai variant across 14 CPU architectures - all updated yesterday. It kills competitors by SHA256 hash, persists through six layers, and hides as a kernel thread. Here's what's inside.
What Gets Deployed via Exposed Docker APIs
Over 1,000 unique IPs scan for exposed Docker APIs every day. A fraction go further. We captured every container creation payload and classified them by monetization strategy.
React2Shell Update: Custom Go L7 DDoS Botnet
A single delivery IP has been exploiting React2Shell to distribute malware from an open directory. 31 binaries including a custom Go L7 DDoS botnet with Cloudflare token forgery, two Mirai variants across 13 CPU architectures, and a C2 server.
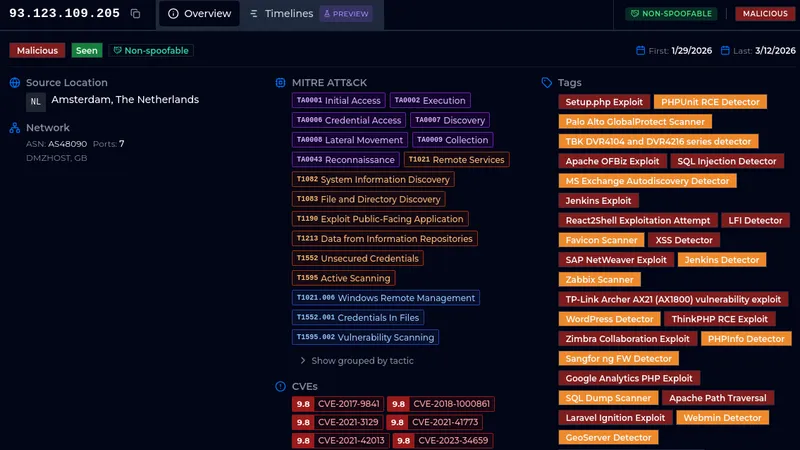
Analyze everything or move straight to network-level blocking?
One IP. Four days. Nearly 900 user agents. Over 3,000 probes. Sometimes a single IP address tells you everything you need to know about how industrialized internet scanning has become.

Coordinated Credential-Stuffing Campaign Targets Palo Alto GlobalProtect Portals
A coordinated credential-stuffing campaign hit GlobalProtect VPN portals with 8,575 IPs in 48 hours. Three attack waves, 78 targeted usernames, one password. Our team breaks down the timeline, infrastructure, fingerprints, and what defenders can do.