Recon & Mass Exploitation Research
Threat research on reconnaissance and mass exploitation activity from ELLIO. Read the latest threat news and defense analysis.
PHP2Shell: attacks before the patch, and automation by nightfall
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including what the attack tooling actually carried.
"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.

ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.
ELLIO Gets a Major Upgrade in Its Recon & Mass Exploitation Intelligence
Today, we’re releasing a major set of improvements to ELLIO Reconnaissance and Mass Exploitation Intelligence.

wp2shell in the Wild: From Patch to Mass Exploitation in Under 48 hours
The ELLIO Deception Network recorded more than 11,500 sessions across 700 sensors as traffic moved from probing to attempted database extraction, administrator creation, and a web-shell write. The first probe arrived the morning after WordPress published its fix.
Sanctioned, Seized, Still Scanning: Inside a Russian Bulletproof Hosting Network Targeting the EU
On 18 May 2026, Dutch investigators seized more than 800 servers and broke up a hosting operation that prosecutors say powered Russian cyberattacks across the EU. We had spent the previous year watching the same network from the other side. After the seizure, the scanning did not stop.
New Integrations for Microsoft Sentinel and MISP
ELLIO is expanding its threat intelligence ecosystem with two new integrations designed for SOC, detection engineering, and threat intelligence workflows: Microsoft Sentinel via TAXII 2.1 and a native MISP integration.
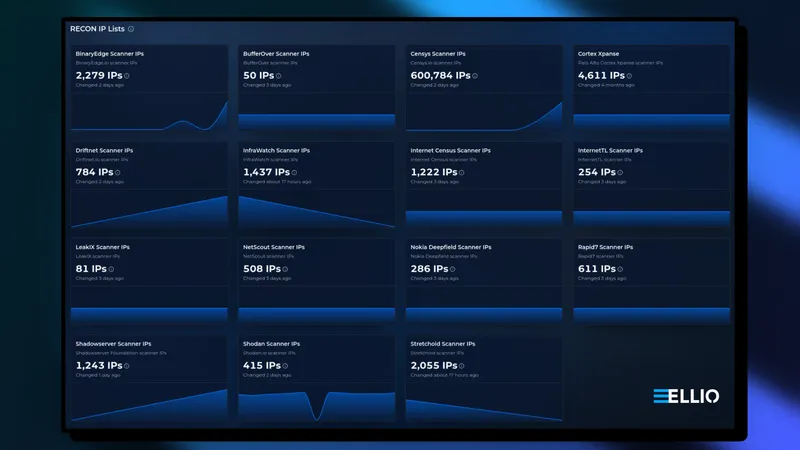
ELLIO expands with 10 new recon and scanner IP feeds
ELLIO Threat Intelligence & Blocklist Automation has been updated with 10 new scanner and recon IP address feeds. This improves detection and control of scanning activity at the network perimeter, enabling more accurate allow and block rules without manual IP range management.
[watchdog]: Inside a Mirai variant with six-layer persistence
An open directory is serving a Mirai variant across 14 CPU architectures - all updated yesterday. It kills competitors by SHA256 hash, persists through six layers, and hides as a kernel thread. Here's what's inside.
What Gets Deployed via Exposed Docker APIs
Over 1,000 unique IPs scan for exposed Docker APIs every day. A fraction go further. We captured every container creation payload and classified them by monetization strategy.