European Threat Intelligence for early-stage attacks.
ELLIO provides direct, first-party observation of live reconnaissance, probing, and exploitation activity from our own global cyber deception network, delivering the fresh context needed to make the right call at the right time.
EU-BUILT THREAT INTELLIGENCE
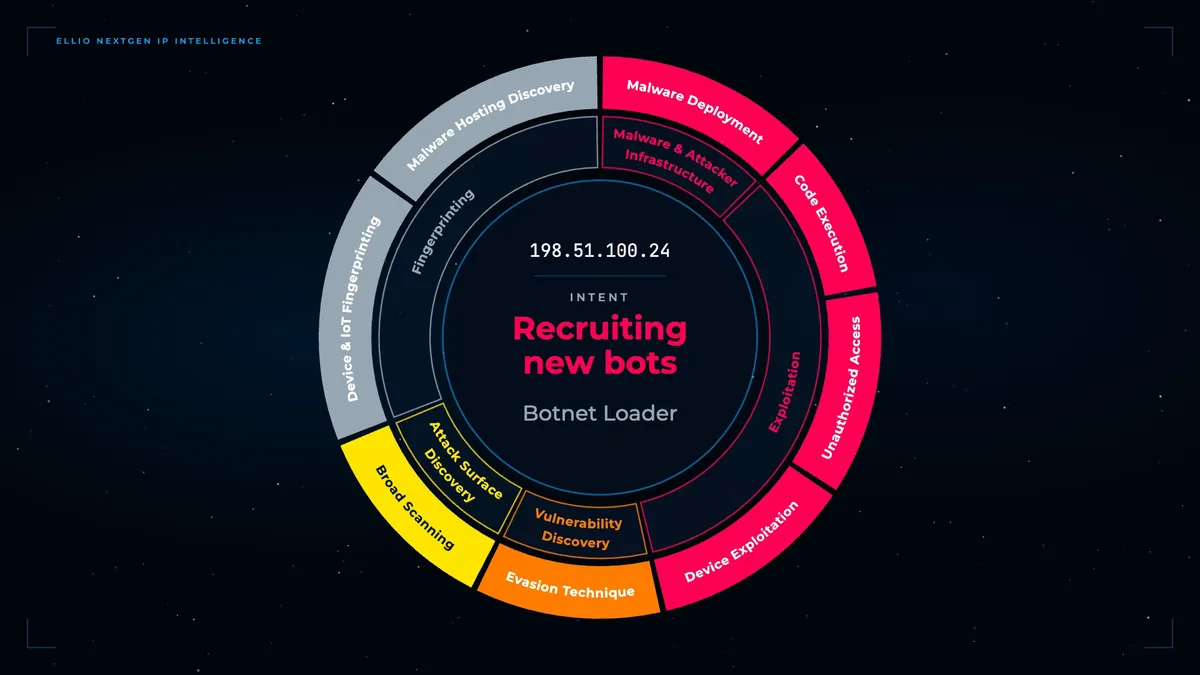
We read reconnaissance
as intelligence, not noise.
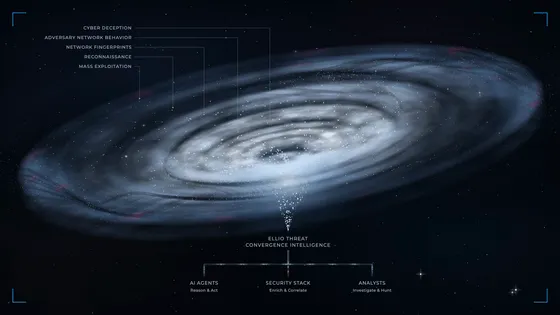
At Internet scale, targeting, probing, infrastructure reuse, and behavioral patterns show where adversary attention is moving and when activity starts to form a campaign. The earlier a threat is understood, the less it costs to contain.
- High-fidelity signals
- Direct observations of live activity
- No third-party data noise
Sovereignty
ELLIO Threat Intelligence is developed and operated in Europe, ensuring independent and trusted threat intelligence.
Alignment with Europe’s Cybersecurity Priorities
We support EU frameworks including NIS2, the Cyber Resilience Act, and Europe’s cyber resilience objectives through actionable real-time threat intelligence.
Data Protection & Privacy
We do not collect customer data for secondary use, AI training, or unrelated analytics. All intelligence is derived from independent threat observation and research.
PHP2Shell: attacks before the patch, and automation by nightfall
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including what the attack tooling actually carried.

"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.
ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.
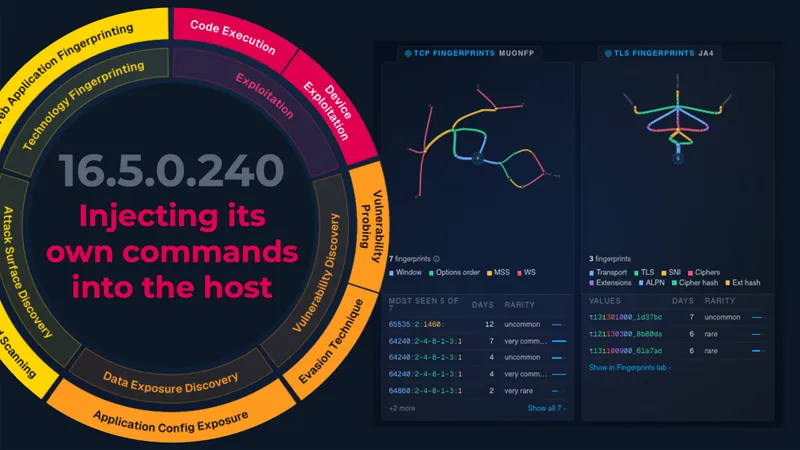
The Intelligence Value of Network Fingerprinting
Two connections come from different IPs. Are they related? Network fingerprints give analysts another way to compare traffic, investigate suspicious activity and make decisions when reputation data offers few answers. But be careful: a fingerprint is only as useful as the interpretation behind it.

Microsoft Security Naming Survival Guide
A quick guide to Microsoft security name changes, helping you make sense of current terms without getting lost in older names.

Why Microsoft Sentinel Feels Noisy: It’s Not Volume, It’s Recon Blindness
Alert fatigue in Microsoft Sentinel is not caused by alert volume alone. It is a context and correlation problem. Read how reconnaissance-aware threat intelligence helps separate internet scanning noise from active exploitation activity to improve signal quality and reduce false-positive incidents.