Defend against mass exploitation and scanning abuse.
Gain visibility into network-wide scanning activity, reduce exposure to exploitation campaigns, and prioritize emerging threats over low-risk, noisy traffic across your ISP/telco networks.
Get answers to critical questions before compromise happens.
ELLIO helps you understand:
Whether your IP space is being used in recon or exploitation campaigns
Which reconnaissance activity is likely to turn into exploitation
Which customers are participating in malicious or botnet activity
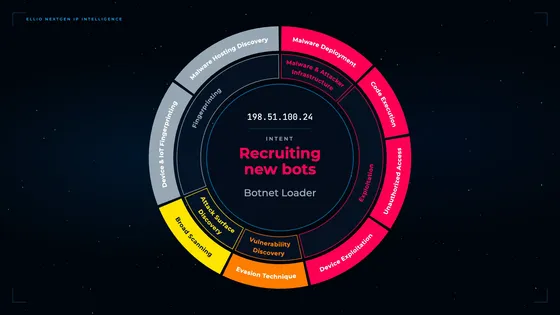
Which signals represent real attacks versus background internet noise
Whether new exploitation attempts appear before patches or detections exist
There is no gap between scan and exploitation activity.
Attackers no longer need time to prepare. They scan, map, and identify weaknesses at machine speed, and move to exploitation immediately once exposure is detected. This compresses the entire attack lifecycle from days to minutes, making post-compromise detection fundamentally too slow to be effective.
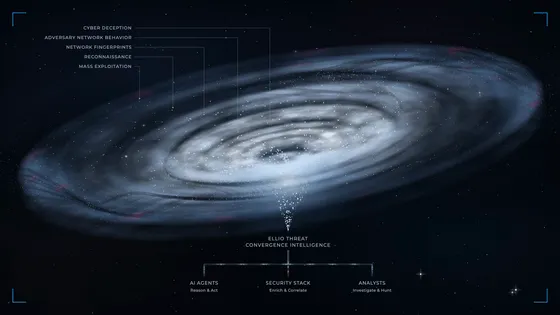
ELLIO provides pre-exploitation telemetry derived from reconnaissance activity, exploitation attempts, and malicious infrastructure behavior observed across global IP space. This enables correlation of scanning patterns, attacker infrastructure reuse, and early-stage exploitation signals targeting ISP/Telco-assigned address space and customer networks, before compromise or service impact occurs.
Reduce risk before it reaches customers and services.
Gain early warning threat intelligence across your networks and prevent service-impacting security incidents.
Network Protection
Reduce exposure of ISP/Telco IP ranges and edge infrastructure by identifying reconnaissance and exploitation activity before it reaches production systems.
Customer Protection
Minimize customer impact by detecting malicious activity and botnet behavior targeting or originating from customer networks earlier in the attack lifecycle.
Security Operation Efficiency
Reduce alert noise by separating background internet scanning from coordinated attack activity, allowing SOC teams to focus on urgent incidents and high-priority activity.
Pre-compromise threat signals for telco-scale security operations.
Protect legitimate traffic, customers, and services by proactively defending against reconnaissance abuse and mass exploitation activity before it leads to impact.
Download the Telecom & ISP Solution Guide.
Overview of ELLIO ASN/IP Monitoring, Blocklist Automation, BGP RTBH and BGP FlowSpec support.
Your download should start automatically.
If it doesn't, click here to download.
PHP2Shell: attacks before the patch, and automation by nightfall
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including what the attack tooling actually carried.

"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.
ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.